
Packet loss happens when data packets sent across a network never reach their destination. You've likely felt it already: a game character jumps backward, a Zoom call turns robotic, or an SSH session freezes and then drops. This guide covers the causes, how to test for it on Windows, macOS, and Linux, and the fixes that work in practice.
The short version is that some of your data is going missing between your device and the server. Your next job is to figure out where it's being lost. Some loss is local (your machine or LAN). Some is remote (somewhere past your router). Most of troubleshooting is working out which one you're dealing with.
📦 What Is Packet Loss?
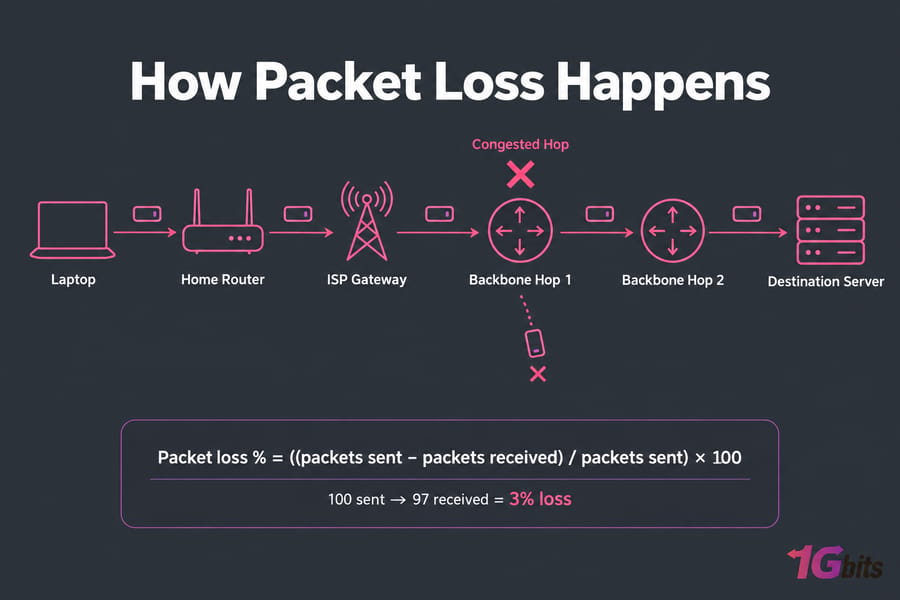
Data on a network doesn't travel as one continuous stream. It gets split into small packets that move hop by hop through routers, switches, firewalls, and ISP links. If any packet is dropped along the way — through congestion, a faulty cable, or a device that's overloaded — you have packet loss.
Each packet contains a header with source and destination IPs, a payload with the actual data, and a trailer with error-checking information. The Transmission Control Protocol splits data into these chunks and reassembles them at the destination.
The metric itself is easy to calculate:
Packet loss % = ((packets sent - packets received) / packets sent) × 100If you send 100 ping packets and get 97 replies, you have 3% packet loss. That may not sound like much, but it's enough to wreck a voice call. A small amount of loss now and then is normal — networks drop packets on purpose to manage congestion. The trouble starts when the loss is persistent or keeps climbing.
⚖️ Packet Loss vs Latency vs Jitter
People mix these three up constantly. I've watched gamers blame "high ping" when packets were actually being dropped. The difference matters because each problem has a different fix.
| Metric | What it measures | What you notice |
| Packet loss | Packets that never arrive | Rubber-banding, audio dropouts, frozen frames, disconnects |
| Latency | Round-trip time (ms) for a packet | Delayed reactions, slow page response |
| Jitter | Variation in latency between packets | Choppy or uneven voice and video |
Latency is how long the trip takes. Packet loss means part of the cargo never shows up. Jitter means the deliveries arrive at uneven intervals. Real-time apps like gaming and VoIP are hurt by all three, but packet loss usually does the most visible damage.
🔍 Common Symptoms
- Gaming: rubber-banding, hits that don't register, sudden teleporting players
- Video and VoIP calls: robotic audio, frozen video, words cut out mid-sentence
- Streaming and browsing: buffering and pages that half-load, even when a speed test looks fine
- Servers: SSH or RDP sessions that hang or drop, and slow file transfers caused by TCP retransmissions
🎯 What Causes Packet Loss?
There are about nine usual suspects. In practice, the first three account for most home and office cases.
- Network congestion: when a link is saturated, routers drop whatever doesn't fit in their buffers. This is the classic cause of degraded VoIP call quality and slow transmission.
- Wi-Fi interference or weak signal: walls, microwaves, neighbouring networks, and distance all corrupt frames. Wireless networks are riskier than wired connections and impact your latency and jitter.
- Faulty cables, ports, or NICs: a crushed Ethernet cable or a worn fibre connector can drop packets intermittently for months before anyone spots it.
- Outdated drivers or firmware: buggy NIC drivers and old router firmware are common and easy to miss.
- Router, switch, or firewall overload: a cheap router that runs out of CPU under load will drop traffic.
- MTU mismatch and fragmentation: packets that are too large for a link on the path get dropped — often hits VPN users.
- Duplex mismatch: one end set to full duplex and the other to half causes collisions and drops.
- ISP or upstream routing issues: congested peering points or a bad route somewhere you can't control.
- Security filtering or DDoS: firewalls and rate limits deliberately dropping traffic, including Denial of Service attacks that overwhelm the link.
You can use network monitoring tools to measure congestion and identify faulty hardware by tracking high latency, elevated jitter, and rising packet loss rates.
🧪 How to Test Packet Loss
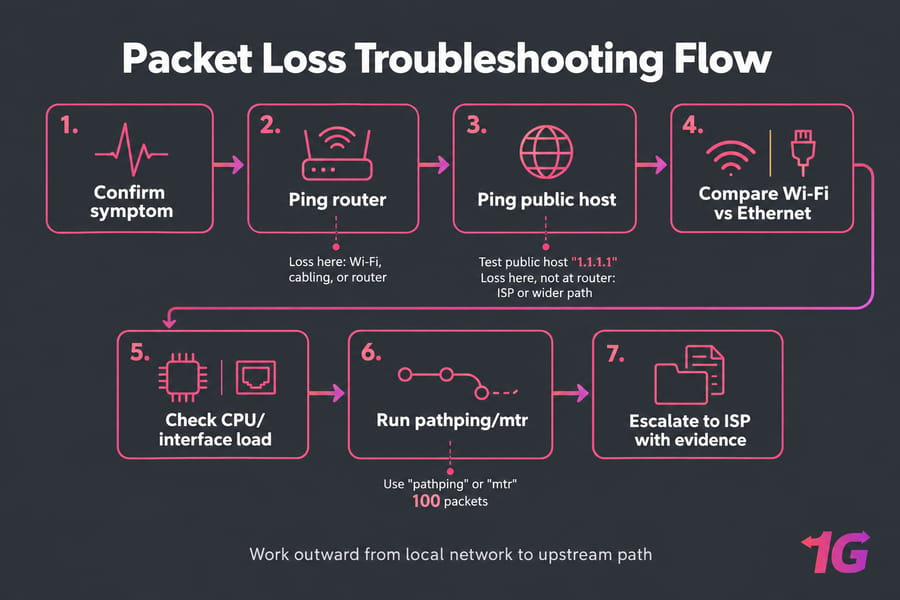
Many guides tell you to run ping 127.0.0.1. That only checks your own TCP/IP stack — it tells you nothing about your internet connection. A better approach is three steps that move outward:
- Ping your router (default gateway). Loss here points to Wi-Fi, cabling, or the router.
- Ping a stable public host such as
1.1.1.1. Loss here but not at the router suggests your ISP or the wider path. - Run a hop-by-hop test (pathping or mtr) to find where the drops start.
Windows
ipconfig                      # find your Default Gateway
ping 192.168.1.1 -n 100       # test the local link
ping 1.1.1.1 -n 100           # test the internet path
pathping 1.1.1.1              # per-hop loss statistics
tracert 1.1.1.1               # list the route
pathping takes a few minutes — be patient. It reports loss at each intermediate hop. For packet-level detail, Windows includes pktmon, a built-in monitor that shows whether a packet was dropped on your own machine.
macOS and Linux
ping -c 100 192.168.1.1
ping -c 100 1.1.1.1
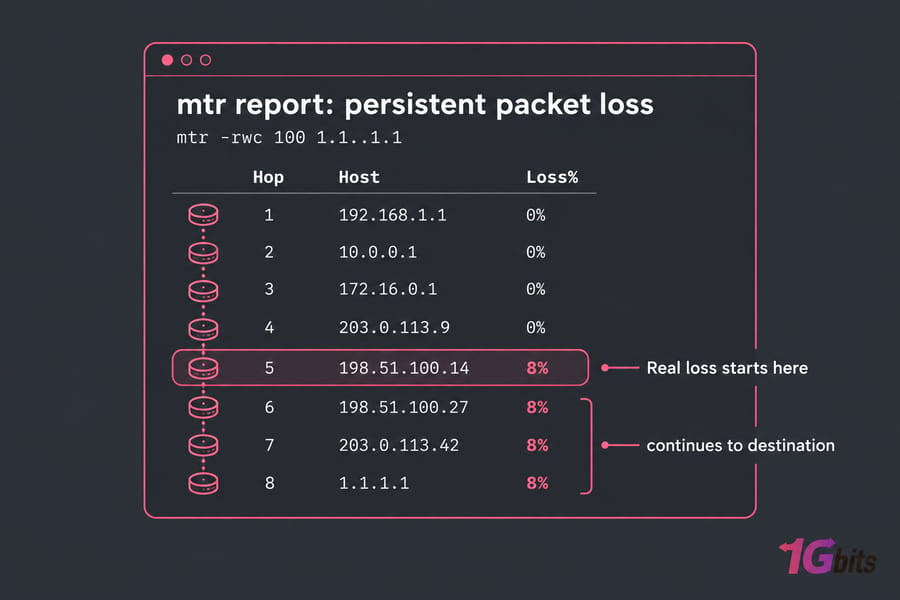
mtr -rwc 100 1.1.1.1          # report mode, 100 cycles
ip -s link                    # Linux: interface errors and drops
On macOS, install mtr with Homebrew. Send at least 100 packets so the result is meaningful — ten pings won't tell you much.
Reading the Results Correctly
Here's a mistake that trips up a lot of people. If one middle hop shows 40% loss but every hop after it shows 0%, that router is just deprioritising ICMP replies — nothing is actually wrong. Real loss starts at a hop and continues all the way to the destination. For packet-level detail, use Wireshark.
🛠️ How to Fix Packet Loss
Start with the easiest fixes and work through them in order:
- Restart and isolate. Reboot the router and modem, then test again with only one device connected.
- Switch to Ethernet. If the loss disappears on a cable, you've found a Wi-Fi problem. Move the router, change channels, or use 5 GHz.
- Swap cables and ports. They're cheap to test and often the cause. Check the jacket on the wire for durability and use proper shielding.
- Update NIC drivers and router firmware. Turn on automatic updates to reduce manual effort.
- Configure QoS. Give voice and gaming traffic priority over backups and downloads.
- Reduce congestion. Pause cloud sync, torrents, and 4K streams while you test. Use network monitoring to find where the congestion is.
- Check MTU and duplex. On Linux, run
ethtool eth0to check duplex. Test MTU with do-not-fragment pings, for exampleping -f -l 1472on Windows. - Escalate with evidence. Send your ISP or hosting provider the mtr or pathping output showing where the loss starts. Support teams act faster on data than on "my internet feels laggy." If an attack is suspected, check the logs, look for suspicious IPs, and block them.
📊 How Much Packet Loss Is Normal?
| Packet loss | What to expect |
| 0% | Ideal |
| Under 1% | Usually fine for browsing and downloads |
| 1–2.5% | Noticeable in games, VoIP, and video calls |
| 3–5% | Real-time apps start to struggle |
| Over 5% | Severe: most things feel broken |
| 100% | No connectivity, or the target blocks ICMP |
🔄 How TCP and UDP Handle Packet Loss
TCP detects missing packets and retransmits them. Downloads and web pages still finish — just more slowly — so the loss is partly hidden. UDP, which most games, VoIP, and video calls use, doesn't retransmit. A lost packet stays lost. That's why real-time apps show packet loss right away while your browser seems fine.
🖥️ Preventing Packet Loss on Servers and VPS
For hosted workloads, prevention mostly comes down to monitoring. Track interface errors and discards, set up alerts for loss above 1%, and keep historical graphs so you can tell a one-off spike from a recurring evening-congestion pattern. Tools like SolarWinds, PRTG, ManageEngine OpManager, and Nagios XI all track latency, loss, and availability. For a single server, a cron job running mtr is often enough.
Network quality also depends on where your server sits. A Linux VPS with full root access lets you run mtr, tcpdump, and ethtool yourself. A scalable cloud VPS in a location close to your users shortens the path, so there are fewer hops where packets can be lost.
🎯 Conclusion
Packet loss refers to the failure of data packets to reach their destination. It shows up as lags in video calls, gaming, or slow-loading web pages, and it usually comes from network congestion, hardware issues, or software conflicts. The fix depends on where the loss actually starts — so run the three-step test before you start swapping cables.
On a stable connection, keep an eye out for loss above 1%. The instant it climbs higher, trace the hops, find where the drops begin, and fix the hop rather than the symptom. That approach solves more problems than any hardware upgrade.

Leave A Comment