
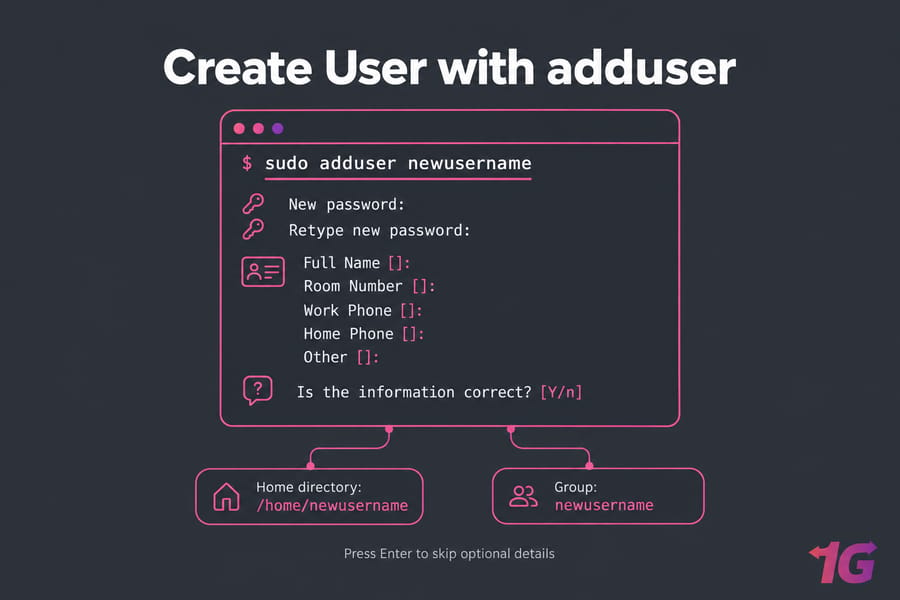
To create a user on Ubuntu, run sudo adduser newusername. It asks you for a password and a few optional details (you can press Enter to skip those). Then it creates the account, a home directory at /home/newusername, and a group with the same name. On most servers, that one command is enough.
sudo adduser newusernameManaging users is a fundamental task in system administration, especially when working with Linux servers. Whether you're setting up a personal project or configuring a multi-user Ubuntu server, understanding how to create user accounts securely is essential. A usable account needs a few more steps: granting sudo, setting up SSH keys, verifying the account, and eventually removing it. This guide covers each of those steps on Ubuntu Server and Desktop, plus the separate steps for WSL.
Want to understand the basics first? Read our article What is Ubuntu before proceeding with user management.
🔒 Why Create a Separate User on Ubuntu?
Working as root every day is a bad habit. One mistyped rm -rf can take down the whole system. When everyone shares the same login, you also can't tell who changed what. I've cleaned up servers where five people shared one root password, and nobody could say who had broken the Nginx config.
The root account has unrestricted access to the entire system, meaning any accidental or malicious command can cause serious damage. Give each person a non-root account. Grant sudo only to the people who need it, and only when they need it. That's least privilege, and it makes auditing much easier.
Creating distinct user accounts also enhances accountability and organization, especially in collaborative environments like development teams, educational institutions, or hosted server applications. With individual user accounts, it's easier to monitor activity, restrict file access, and apply user-specific settings and permissions.
⚖️ adduser vs useradd in Ubuntu
Ubuntu has two tools for creating users, and people confuse them all the time. adduser is a friendly, interactive wrapper that calls useradd behind the scenes. Debian's own man page recommends it for everyday use. useradd is the low-level tool. It does only what its flags tell it to do.
| Feature | adduser | useradd |
| Interactive prompts | Yes | No |
| Home directory | Created automatically | Only with -m |
| Default shell | Set from /etc/adduser.conf |
Set with -s or from /etc/default/useradd |
| Password | Prompted | Set separately with passwd |
| Best for | Manual admin work | Scripts, automation, special cases |
My rule: use adduser when you're typing commands yourself and useradd inside scripts. If you're still deciding which distro to base your workflow on, our Debian vs Ubuntu comparison is worth a read first.
🛠️ How to Create a User from the Command Line
Create a user with useradd
sudo useradd -m -s /bin/bash newusername
sudo passwd newusername
-m creates the home directory, and -s sets the login shell. If you leave out -s, the shell may default to /bin/sh. The user then ends up with no tab completion and a bare prompt, which is confusing for them.
Custom home directory, shell, or UID
sudo useradd -m -d /srv/appuser -s /bin/zsh -u 1500 appuserCreate a system user (service account)
Services like a background worker or a backup agent don't need a human login:
sudo adduser --system --group --no-create-home appserviceWant a broader overview? Check out our detailed guide on How to create users in Linux.
🔑 How to Give a User Sudo Privileges
On Ubuntu, the standard way to give a user full admin rights is to add them to the sudo group:
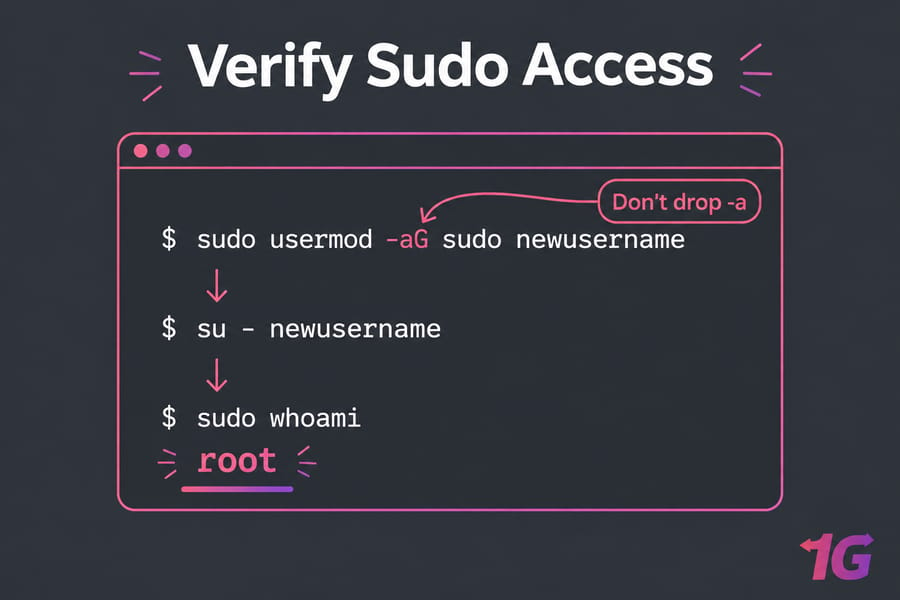
sudo usermod -aG sudo newusernameDon't drop the -a. Without it, -G replaces the user's supplementary groups instead of adding to them. Only edit sudoers through visudo when you need fine-grained rules.
Test sudo access safely
su - newusername
sudo whoami
sudo -l
If sudo whoami prints root, sudo works. Keep your original session open until you've confirmed this, so you can still fix things if it doesn't.
Need a deeper explanation of permissions? See our article on Add users to Sudoers.
👥 How to Add a User to a Group
Adding a user to a group is a powerful way to assign permissions and organize access across services, directories, and system resources. Groups in Ubuntu are often used to manage access to specific software (like Docker), directories (like shared project folders), or functionalities (like administrative rights).
sudo usermod -aG docker newusername
sudo groupadd developers
sudo usermod -aG developers newusername
Shared groups like developers or www-data are a clean way to give a team access to a project directory without using chmod 777. After adding a user to a group, log out and log back in for the changes to take effect.
Explore our dedicated article on how to add users on Ubuntu for more group-related best practices.
✅ How to Verify the New User Was Created Correctly
Most people skip this step. Run the following checks:
id newusername: shows the UID, GID and every groupgroups newusername: quick group checkgetent passwd newusername: shows the home directory and login shell (reads/etc/passwdand LDAP, if you use it)ls -ld /home/newusername: confirms the home directory exists and the new user owns it
If getent shows /usr/sbin/nologin or /bin/sh when you expected bash, fix it with sudo usermod -s /bin/bash newusername.
🚫 How to Create a User Without a Password
In some scenarios, especially in automated systems or cloud environments, you may want to create a user account without setting a password. This is common when SSH key authentication is used instead of passwords or when third-party identity providers manage logins.
sudo adduser newuser --disabled-passwordUse this for accounts that should only ever log in with SSH keys. Be careful, though. A disabled password doesn't block SSH key logins. Ubuntu's user management documentation says that to fully cut off SSH access, you need to remove or rename the user's ~/.ssh directory. You should also look for open sessions with w and end them.
🔐 How to Set Up SSH Key Access for a New User
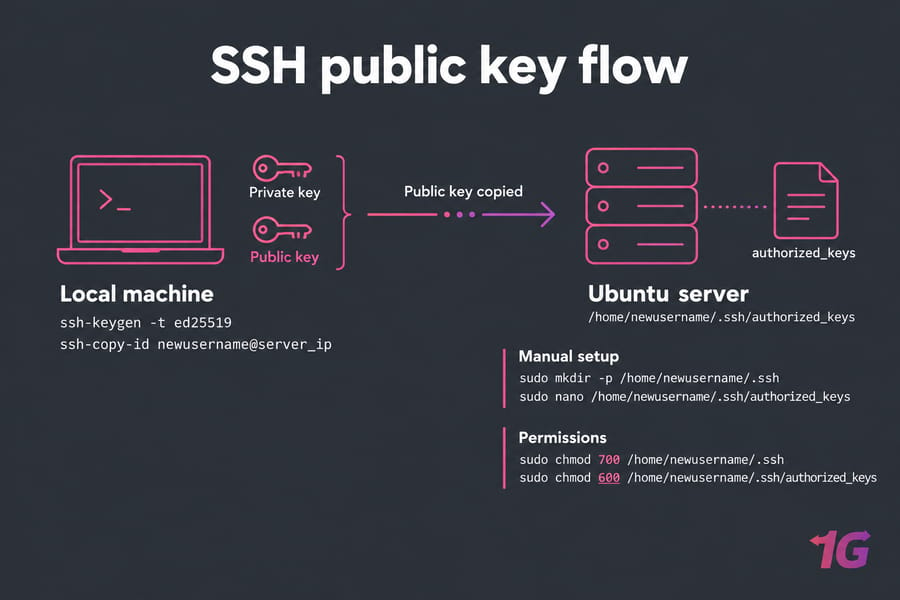
Generate an ed25519 key on your local machine, then copy it to the server:
ssh-keygen -t ed25519
ssh-copy-id newusername@server_ip
If password login is already disabled on the server, add the key manually as root:
sudo mkdir -p /home/newusername/.ssh
sudo nano /home/newusername/.ssh/authorized_keys
sudo chown -R newusername:newusername /home/newusername/.ssh
sudo chmod 700 /home/newusername/.ssh
sudo chmod 600 /home/newusername/.ssh/authorized_keys
Those permissions matter. If the directory or file can be written by others, OpenSSH ignores your key, and the error message doesn't say why. To limit who can log in, add an AllowGroups line to /etc/ssh/sshd_config.
📋 How to List Users in Ubuntu
cut -d: -f1 /etc/passwd
compgen -u
getent passwd {1000..60000} | cut -d: -f1
The first two commands list every account, including system users like www-data and sshd. On Ubuntu, regular human accounts start at UID 1000, so the third command shows only those. For more detailed insights, check out our guide on how to list users in Ubuntu.
🔒 How to Lock, Disable, or Delete a User
Locking an account keeps all its data but blocks password logins. Deleting removes the account itself.
sudo passwd -l username          # lock password
sudo usermod -L username         # same effect
sudo usermod -e 1 username       # expire account entirely
sudo deluser username            # delete, keep home directory
sudo deluser --remove-home username   # delete and wipe home directory
When someone leaves a team, I lock their account first and delete it a few weeks later. That way, files nobody remembered they owned aren't lost straight away.
💻 How to Create a User in Ubuntu on WSL
Inside WSL, create the user the same way: sudo adduser wsluser. To make it the default login, run this from PowerShell:
ubuntu config --default-user wsluserThat launcher command only works for Ubuntu installed from the Store. If you imported the distro with wsl --import, add this to /etc/wsl.conf instead, then run wsl --shutdown:
[user]
default=wsluser
Recent WSL versions also support wsl --manage Ubuntu --set-default-user wsluser. See Microsoft's WSL basic commands page for the current syntax.
🩺 Common Errors and Troubleshooting
"user already exists"
Check with getent passwd username. Pick another name, or change the existing account with usermod.
User can't use sudo
Run groups username. If sudo isn't listed, run usermod -aG sudo again, and this time include -a.
Group change not applied
Group membership only updates when the user logs in. Log out and back in, or run newgrp groupname. This one catches people every week.
No home directory created
This happens when you use useradd without -m. Fix it with sudo mkhomedir_helper username.
Permission denied
Usually you've forgotten sudo, or the user doesn't own their home directory. Check with ls -ld and fix with chown. If you need a clean Ubuntu instance to practice on without risking your main server, an Ubuntu RDP server with remote desktop access is the fastest way to spin one up.
🎯 Final Thoughts
Creating and managing users in Ubuntu is essential for maintaining a secure, scalable, and well-organized system. Whether you're using an Ubuntu desktop, a server environment, or WSL, the process is nearly identical and straightforward when you follow best practices.
With this guide, you've learned how to use command-line tools to create users, assign sudo privileges, add users to groups, and work with Ubuntu server and WSL environments. Once you've created a sudo user and set up key-based SSH, the next steps are to disable root SSH login, turn on UFW, and review your group memberships regularly. If you need a fresh install to practice on, our guide on how to install Ubuntu from USB covers the setup end-to-end.
Ready to take full control of your Ubuntu experience? Explore our Ubuntu VPS Hosting solutions and start managing your own server environment today.
People also read:

Leave A Comment